The module lifecycle stage: General Availability
Standard
- An internal cluster network is created with a gateway to the public network.
- The elastic IP can be assigned to the master node.
- Nodes managed by the Cluster API do not have public IP addresses.
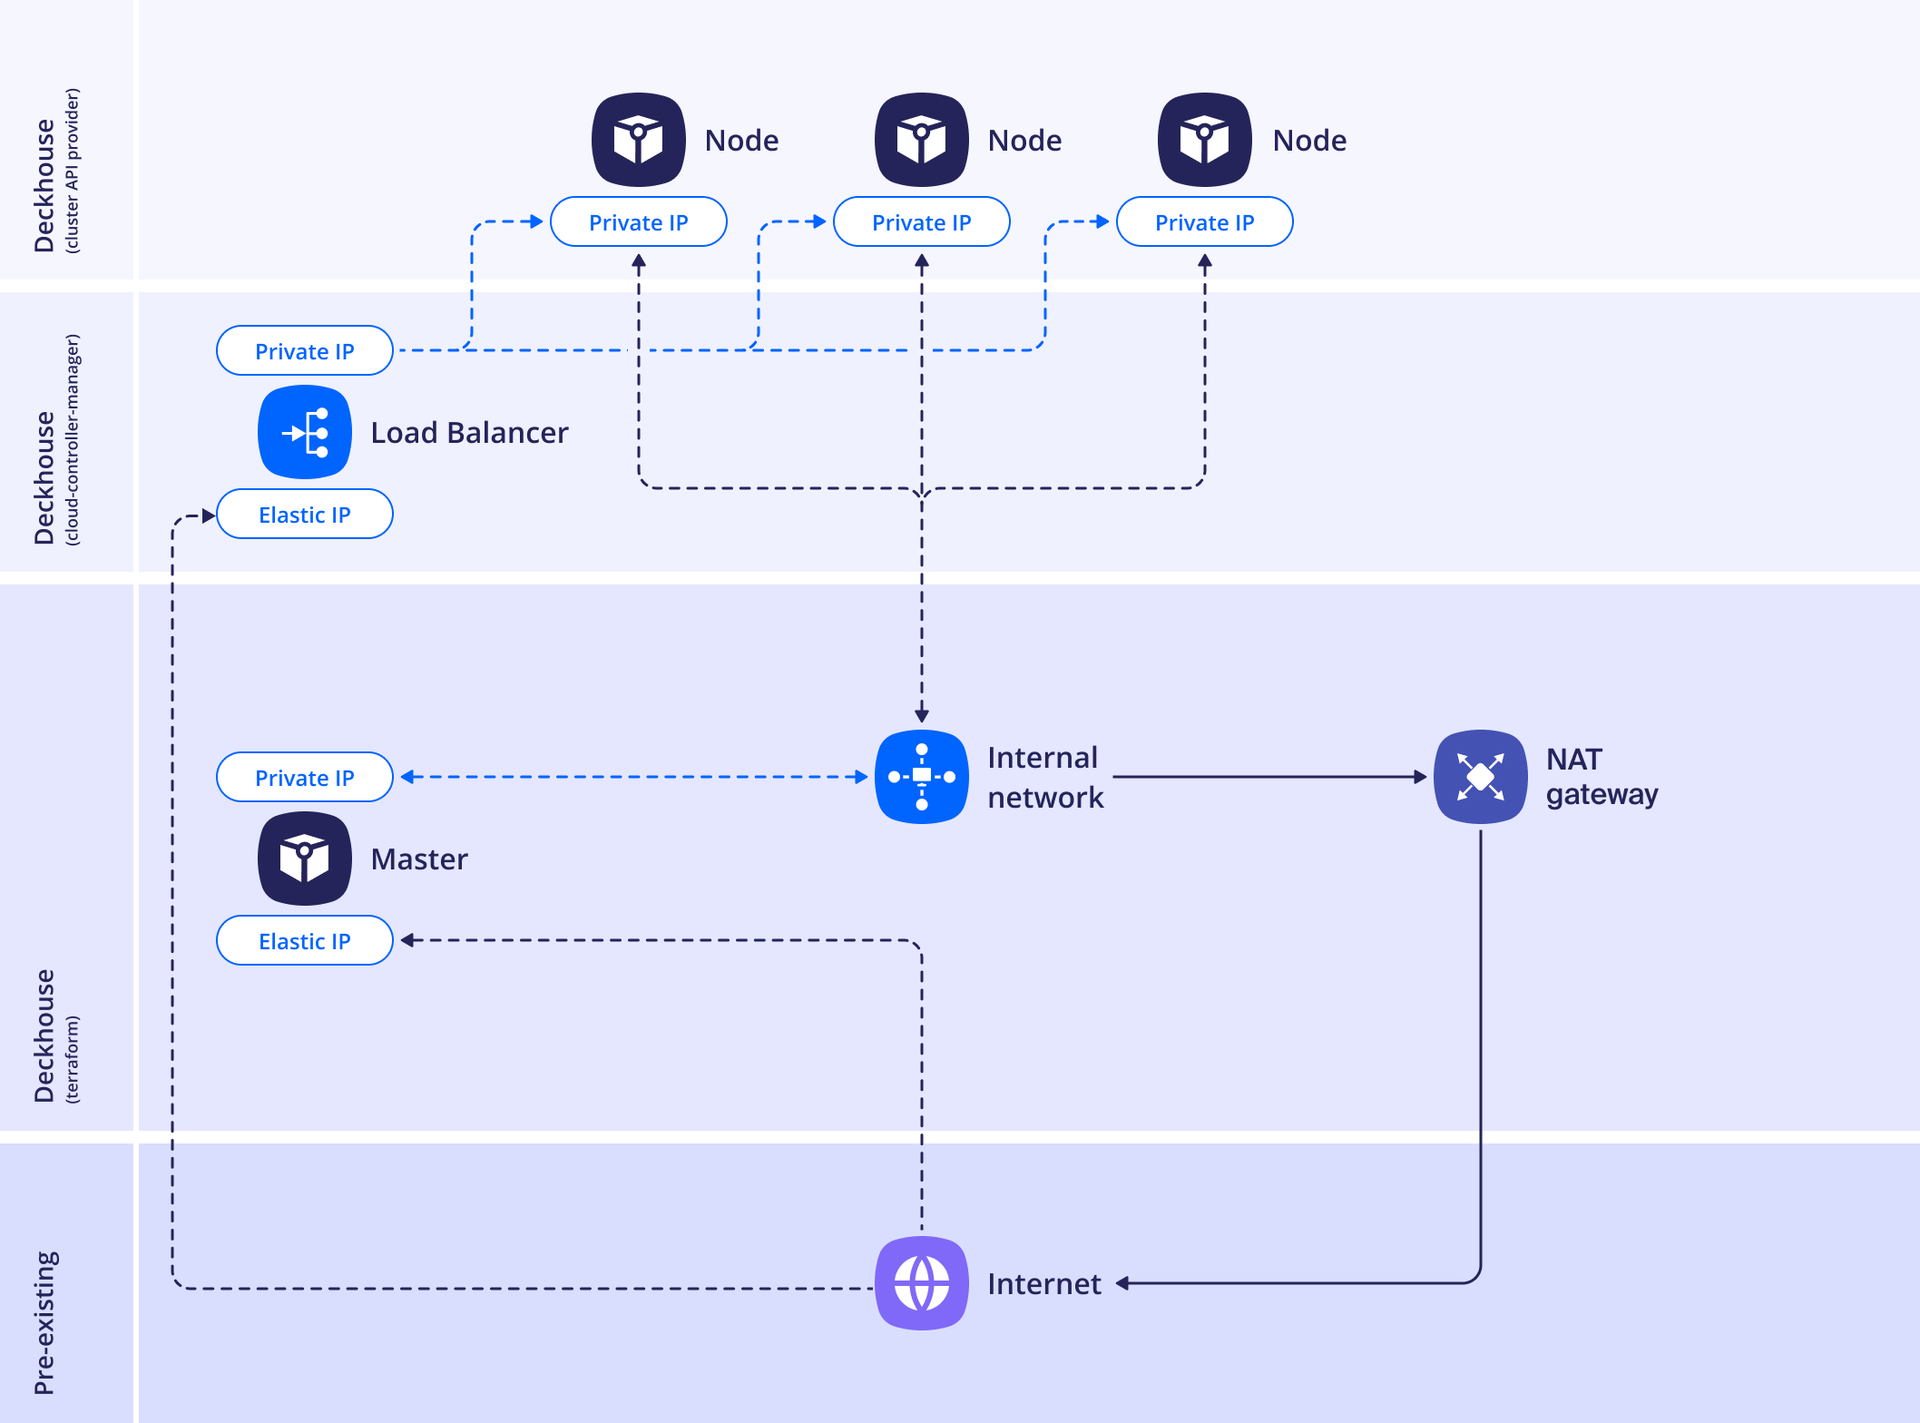
The internalNetworkSecurity parameter (default true) enables the creation of a security group (SecurityGroup) when a cluster is created. The module creates the group named after the cluster prefix and assigns it to the nodes.
The following inbound rules will be created:
- allow incoming traffic over the TCP protocol on port
22from0.0.0.0/0 - allow incoming traffic over the ICMP protocol from
0.0.0.0/0 - allow incoming traffic over the TCP protocol on ports
30000–32767for services of theNodePorttype. Inbound UDP traffic toNodePortports is not allowed by default
Attach custom security groups for CloudEphemeral nodes in the HuaweiCloudInstanceClass resource via spec.securityGroups. They are applied together with the group created by the module.
Example of the layout configuration:
apiVersion: deckhouse.io/v1
kind: HuaweiCloudClusterConfiguration
layout: Standard
sshPublicKey: "<SSH_PUBLIC_KEY>"
standard:
  internalNetworkDNSServers:
    - 8.8.8.8
  internalNetworkCIDR: 192.168.199.0/24
  internalNetworkSecurity: true
  enableEIP: true
provider:
  cloud: hc.sbercloud.ru
  region: ru-moscow-1
  accessKey: "<Access key>"
  secretKey: "<Secret key>"
  projectID: "<Project ID>"
masterNodeGroup:
  replicas: 1
  instanceClass:
    imageName: alt-p11
    flavorName: s7n.xlarge.2
    rootDiskSize: 50
  serverGroup:
    policy: AntiAffinity
  volumeTypeMap:
    ru-moscow-1a: SSD
VpcPeering
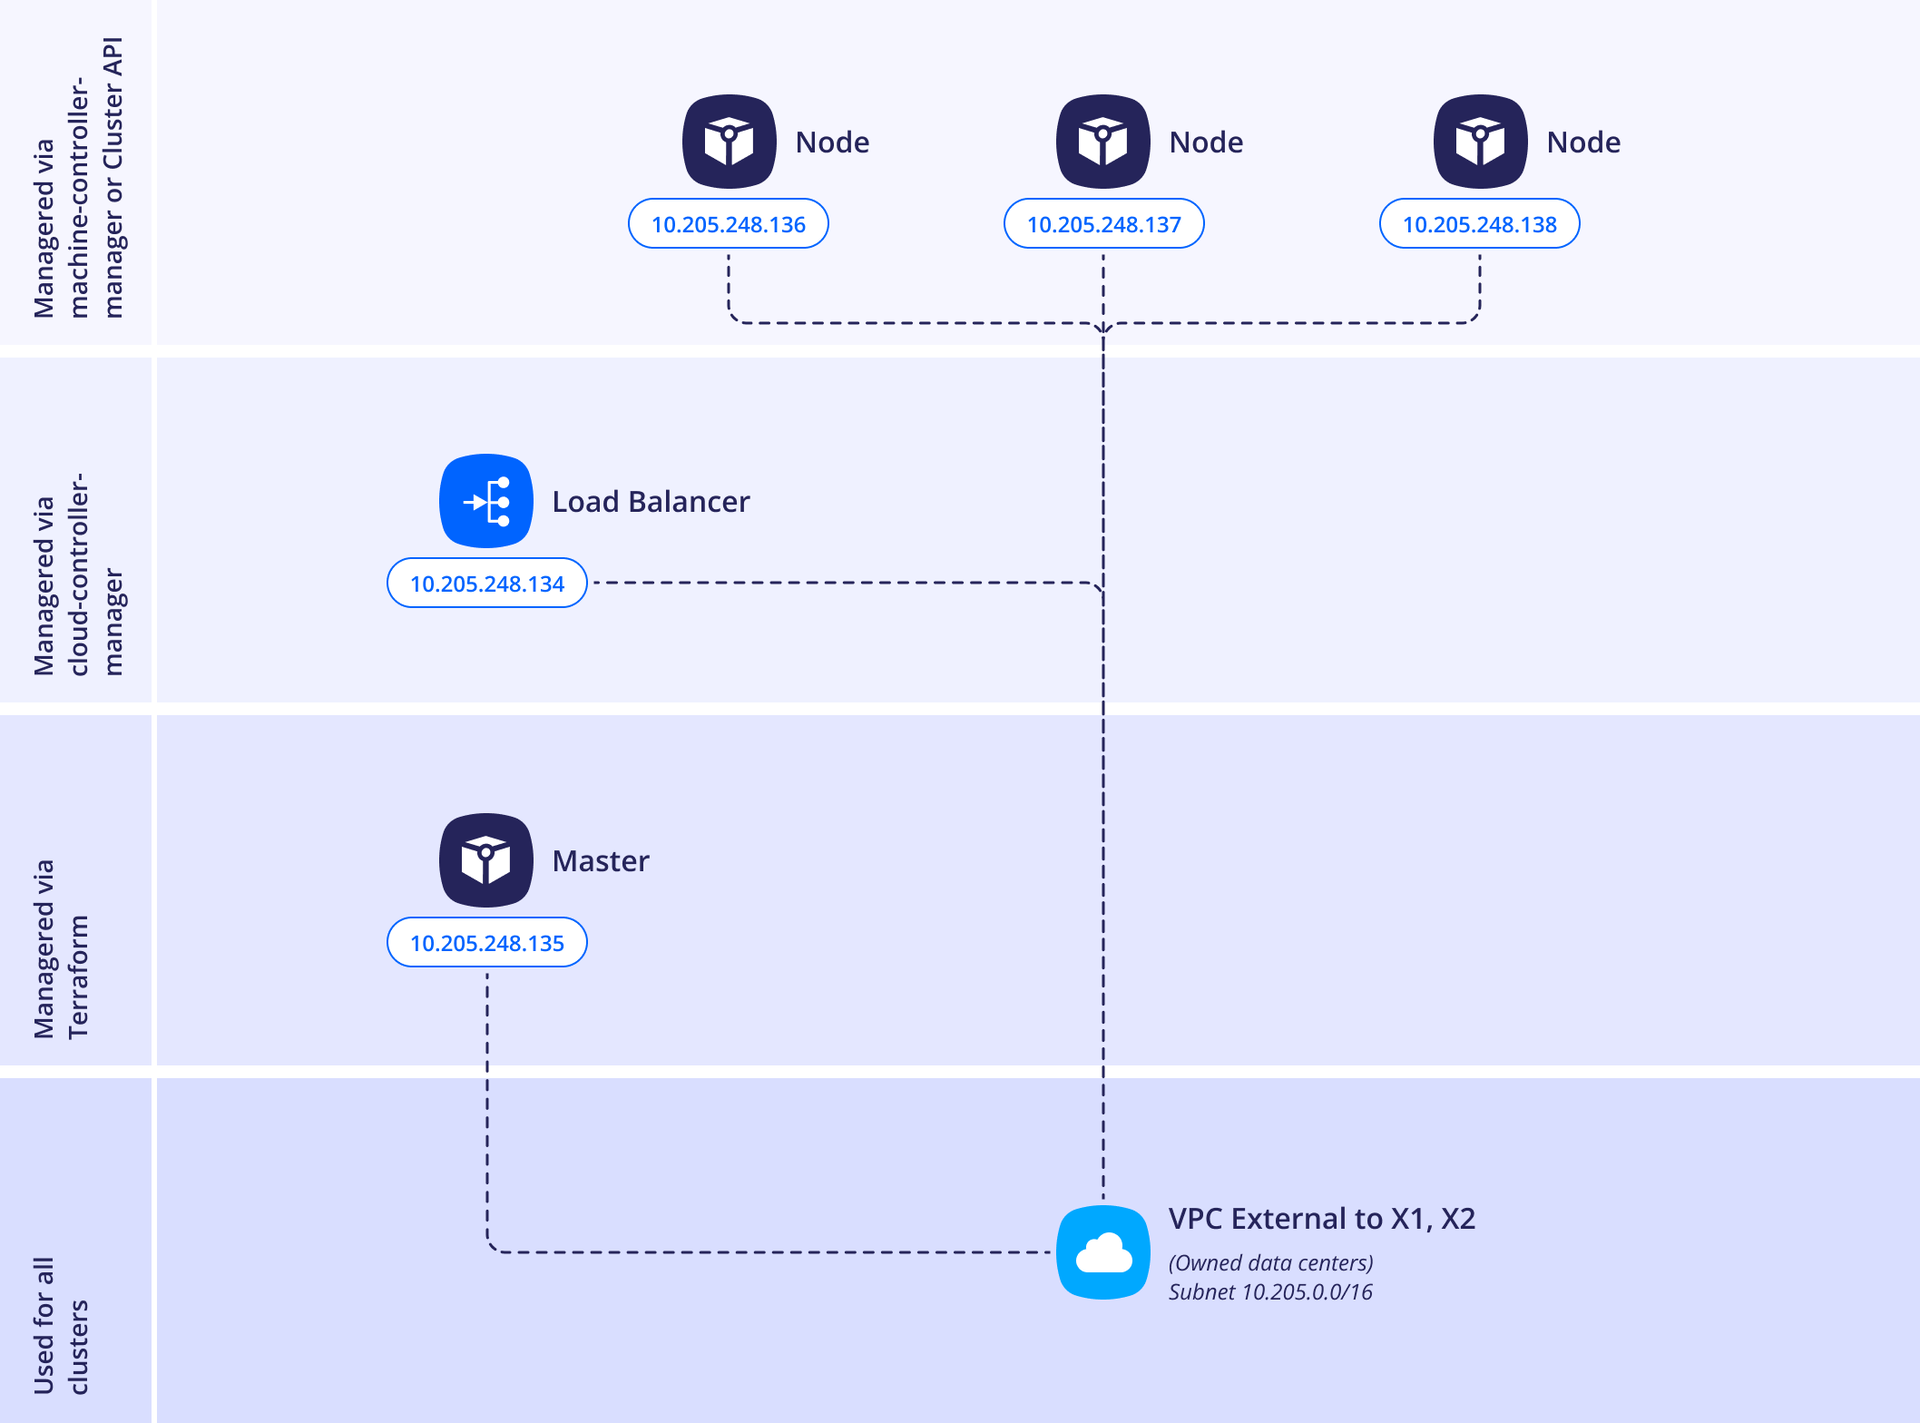
The internalNetworkSecurity parameter (default true) enables the creation of a security group (SecurityGroup) when a cluster is created. The module creates the group named after the cluster prefix and assigns it to the nodes.
The following inbound rules will be created:
- allow incoming traffic over the TCP protocol on port
22from0.0.0.0/0 - allow incoming traffic over the ICMP protocol from
0.0.0.0/0 - allow incoming traffic over the TCP protocol on ports
30000–32767for services of theNodePorttype. Inbound UDP traffic toNodePortports is not allowed by default
Attach custom security groups for CloudEphemeral nodes in the HuaweiCloudInstanceClass resource via spec.securityGroups. They are applied together with the group created by the module.
Example of the layout configuration:
apiVersion: deckhouse.io/v1
kind: HuaweiCloudClusterConfiguration
layout: VpcPeering
sshPublicKey: "<SSH_PUBLIC_KEY>"
vpcPeering:
  internalNetworkDNSServers:
    - 8.8.8.8
  internalNetworkCIDR: 10.221.128.0/24
  internalNetworkSecurity: true
  subnet: subnet-43b4