Available in: Ultimate/EE
Included in extensions: Advanced Infrastructure Security
The module lifecycle stage: Generally available version
The module has requirements for installation
How to explicitly enable or disable the module…
You may explicitly enable or disable the module in one of the following ways:
-
Via Deckhouse web UI. In the “System” → “System Management” → “Deckhouse” → “Modules” section, open the
operator-trivymodule and enable (or disable) the “Module enabled” toggle. Save changes.Example:
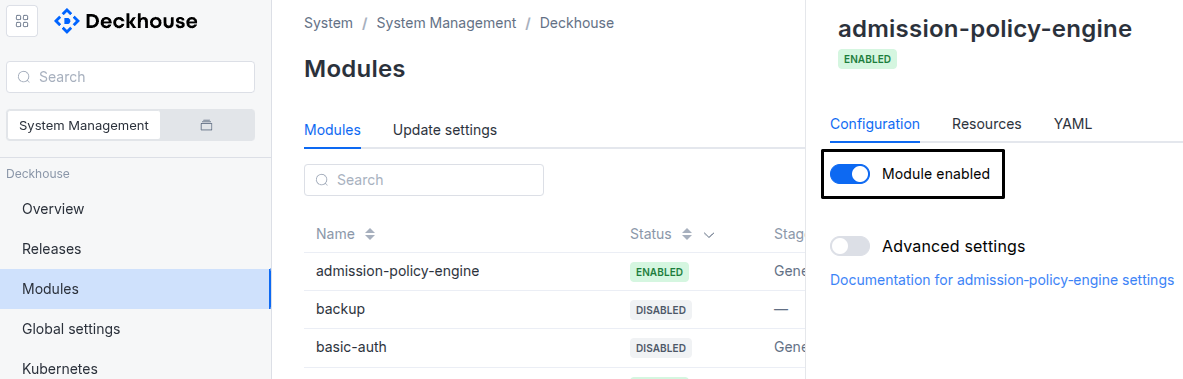
-
Via Deckhouse CLI (d8).
Use the d8 system module enable command for enabling, or d8 system module disable command for disabling the module (you need Deckhouse CLI (d8), configured to work with the cluster).
Example of enabling the module:
d8 system module enable operator-trivy -
Using ModuleConfig
operator-trivy.Set
spec.enabledtotrueorfalsein ModuleConfigoperator-trivy(create it if necessary).Example of a manifest to enable module
operator-trivy:apiVersion: deckhouse.io/v1alpha1 kind: ModuleConfig metadata: name: operator-trivy spec: enabled: true
You can configure the module in one of the following ways:
-
Via Deckhouse web UI.
In the “System” → “System Management” → “Deckhouse” → “Modules” section, open the
operator-trivymodule and enable the “Advanced Settings” toggle. Fill in the required fields in the “Configuration” tab or specify the module settings in YAML format on the “YAML” tab, without the top-levelsettingskey. Save the changes.Example:
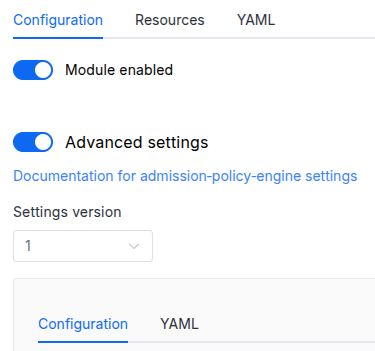
You can also edit the ModuleConfig object
operator-trivyon the “YAML” tab in the module settings window (“System” → “System Management” → “Deckhouse” → “Modules”, open the moduleoperator-trivy) by specifying the schema version in thespec.versionparameter and the necessary module parameters in thespec.settingssection. -
Via Deckhouse CLI (d8) (requires Deckhouse CLI (d8) configured to work with the cluster).
Edit the existing ModuleConfig
operator-trivy(for more details on configuring Deckhouse Platform, see the documentation) by executing the following command:d8 k edit mc operator-trivyMake the necessary changes in the
spec.settingssection. If necessary, specify the schema version in thespec.versionparameter. Save the changes.You can also create a manifest file for ModuleConfig
operator-trivyusing the example below. Fill in thespec.settingssection with the required module parameters. If necessary, specify the schema version in thespec.versionparameter.Apply the manifest using the following command (indicate the manifest file name):
d8 k apply -f <FILENAME>Example of a manifest for ModuleConfig
operator-trivy:apiVersion: deckhouse.io/v1alpha1 kind: ModuleConfig metadata: name: operator-trivy spec: version: 2 enabled: true settings: # Module parameters from the "Parameters" section below.
Requirements
To the Deckhouse Platform version: 1.76 and above.
Conversions
The module is configured using the ModuleConfig resource, the schema of which contains a version number. When you apply an old version of the ModuleConfig schema in a cluster, automatic transformations are performed. To manually update the ModuleConfig schema version, the following steps must be completed sequentially for each version:
-
Updates from version 1 to 2:
nodeScanning.scannersandnodeScanning.pkgTypesnow use PascalCase values (Vuln/Secret,OS/Library). When upgrading to a new version, you need to change the values of the parameters (vuln/secret,os/library), make the values capitalized.
Parameters
Schema version: 2
-
-
array of objectssettings.additionalRegistryCA
List of CA certificates of private container registries.
To specify a certificate chain, for example a certificate with an intermediate CA, put all certificates of the chain one after another in one
cafield, without blank lines between them. The module trusts the certificates from all entries of the list.Example:
additionalRegistryCA: - name: example CA ca: | -----BEGIN CERTIFICATE----- ................. -----END CERTIFICATE----- - name: CA with intermediate CA ca: | -----BEGIN CERTIFICATE----- ................. -----END CERTIFICATE----- -----BEGIN CERTIFICATE----- ................. -----END CERTIFICATE------
stringsettings.additionalRegistryCA.caCA certificate or certificate chain in PEM format.
-
stringsettings.additionalRegistryCA.nameArbitrary name of the entry.
-
-
array of stringssettings.additionalVulnerabilityReportFieldsList of additional fields from the vulnerability database to add to VulnerabilityReport objects.
Example:
additionalVulnerabilityReportFields: - Class - Target -
stringsettings.apiServerStorageClass
Name of the StorageClass used to store the
security-storagedata: the scan reports served through thetrivy.deckhouse.ioAPI and, ifnodeAgent.enabledistrue, the runtime map objects.If the value is not specified, the StorageClass will be used according to the global storageClass parameter setting.
The global
storageClassparameter is only considered when the module is enabled. Changing the globalstorageClassparameter while the module is enabled will not trigger disk re-provisioning.Warning. Specifying a value different from the one currently used (in the existing PVC) will result in disk re-provisioning and all data will be deleted.
If
falseis specified,emptyDirwill be forced to be used.Examples:
apiServerStorageClass: ceph-ssdapiServerStorageClass: 'false' -
objectsettings.complianceReportsSettings of the compliance reports deployed by the module.
Default:
{}-
array of stringssettings.complianceReports.enabled
List of compliance frameworks for which the module deploys ClusterComplianceReport objects:
CIS: CIS Kubernetes Benchmark v1.12.PCI-DSS: PCI DSS v4.0 (key controls for protecting cardholder data).NSA: NSA-CISA Kubernetes Hardening Guidance v1.0.GDPR: General Data Protection Regulation (key security-relevant articles).HIPAA: HIPAA Security Rule (key technical safeguards).FSTEC-21: Order of FSTEC of Russia No. 21 (personal data protection in personal data information systems).FZ-187: Order of FSTEC of Russia No. 239 (security requirements for significant CII objects, Federal Law 187-FZ).
Default:
[
 "CIS",
 "PCI-DSS",
 "NSA",
 "FSTEC-21",
 "FZ-187"
]
Examples:
enabled: - CIS - NSAenabled: - CIS - PCI-DSS - NSA - GDPR - HIPAA - FSTEC-21 - FZ-187-
stringsettings.complianceReports.enabled.Element of the array
Allowed values:
CIS,PCI-DSS,NSA,GDPR,HIPAA,FSTEC-21,FZ-187
-
booleansettings.complianceReports.skipSystemResources
Exclusion of system objects from configuration audit and RBAC assessment reports.
If the parameter is
true, the module does not create the following reports:- ConfigAuditReport and RbacAssessmentReport in namespaces that match
d8-*,kube-*ordefault - ClusterConfigAuditReport and ClusterRbacAssessmentReport for cluster-scoped objects with the
heritage=deckhouselabel (objects managed by Deckhouse Platform (DP)) or thekubernetes.io/bootstrapping=rbac-defaultslabel (built-in Kubernetes RBAC objects, such ascluster-adminand thesystem:*roles)
Findings for objects with these labels are also excluded from ClusterComplianceReport objects.
The parameter does not affect VulnerabilityReport, ExposedSecretReport, SbomReport and InfraAssessmentReport objects.
To exclude a namespace from configuration audit and RBAC assessment reports regardless of this parameter, add the
security.deckhouse.io/skip-compliance=truelabel to the Namespace.Default:
trueExamples:
skipSystemResources: trueskipSystemResources: false - ConfigAuditReport and RbacAssessmentReport in namespaces that match
-
-
integersettings.concurrentScanJobsLimitMaximum number of scan jobs that the operator can run concurrently.
Default:
10Allowed values:
1 <= XExamples:
concurrentScanJobsLimit: 3concurrentScanJobsLimit: 5concurrentScanJobsLimit: 10 -
objectsettings.denyVulnerableImages
Settings for blocking the creation of Pod, Deployment, StatefulSet, DaemonSet and OpenKruise DaemonSet objects with vulnerable images in namespaces with the
security.deckhouse.io/trivy-provider: ""label.Note. The check runs only when an object is created or updated. The Gatekeeper audit does not check existing objects against this constraint.
Default:
{}-
array of stringssettings.denyVulnerableImages.allowedSeverityLevels
Severity levels of vulnerabilities that do not block an image.
An image that contains only vulnerabilities of these levels is not blocked.
-
stringsettings.denyVulnerableImages.allowedSeverityLevels.Element of the array
Allowed values:
UNKNOWN,LOW,MEDIUM,HIGH,CRITICAL
-
-
booleansettings.denyVulnerableImages.enabledEnables blocking of vulnerable images in namespaces with the
security.deckhouse.io/trivy-provider: ""label.Default:
false -
array of objectssettings.denyVulnerableImages.registrySecrets
List of additional Secrets with credentials of private container registries, used to download images for scanning.
Each Secret must be of type
kubernetes.io/dockerconfigjson. The credentials of the container registry that Deckhouse Platform (DP) is installed from are always used.Default:
[]-
stringsettings.denyVulnerableImages.registrySecrets.nameName of the Secret.
-
stringsettings.denyVulnerableImages.registrySecrets.namespaceNamespace of the Secret.
-
-
-
booleansettings.disableSBOMGeneration
Disables SBOM reports generation.
Warning. When this option is set to
true, all current SBOM reports are deleted from the cluster. The cleanup is executed only once.Default:
falseExamples:
disableSBOMGeneration: truedisableSBOMGeneration: false -
booleansettings.insecureDbRegistryAllows Trivy to download vulnerability databases using insecure HTTPS connections (not passed TLS certificate verification) or HTTP connections.
Default:
falseExamples:
insecureDbRegistry: trueinsecureDbRegistry: false -
array of stringssettings.insecureRegistriesList of container registry addresses to which insecure HTTPS connections (not passed TLS certificate verification) or HTTP connections are allowed.
Example:
insecureRegistries: - my.registry.com - http-only.registry.io -
booleansettings.linkCVEtoBDU
Replaces CVE identifiers in VulnerabilityReport objects with the matching identifiers from the FSTEC of Russia Data Bank of Security Threats (BDU).
A vulnerability without a BDU match keeps its CVE identifier.
Default:
falseExamples:
linkCVEtoBDU: truelinkCVEtoBDU: false -
objectsettings.nodeAgent
Runtime application and network map (in preview).
When enabled, a privileged eBPF agent runs on every node and observes the runtime behaviour of each workload: the processes it launches, the files it opens, the Linux capabilities and system calls it uses, and the network connections it makes. The observations are aggregated per workload into ApplicationProfile and NetworkNeighborhood objects.
Requirements. Node kernels must be Linux 5.4 or newer and expose BTF at
/sys/kernel/btf/vmlinux. The agent runs privileged with host PID access.Default:
{}-
booleansettings.nodeAgent.enabledEnables runtime observation and building of the application/network map.
Default:
falseExamples:
enabled: trueenabled: false -
objectsettings.nodeAgent.generatePolicies
Generation of least-privilege policies from the runtime map.
The map itself (ApplicationProfile and NetworkNeighborhood objects) is always built when
nodeAgentis enabled. These parameters additionally publish policies generated from it.Default:
{}-
booleansettings.nodeAgent.generatePolicies.networkPolicy
Enables publishing of GeneratedNetworkPolicy objects: NetworkPolicy definitions computed from the NetworkNeighborhood of each workload.
Review a generated policy and apply it to allow the workload only the observed network connections.
Default:
falseExamples:
networkPolicy: truenetworkPolicy: false -
booleansettings.nodeAgent.generatePolicies.seccomp
Enables generation and publishing of SeccompProfile objects from the system calls observed for each workload.
Attach a profile to the workload pods to restrict the allowed system calls.
Default:
falseExamples:
seccomp: trueseccomp: false
-
-
stringsettings.nodeAgent.learningPeriod
Duration of workload observation before the workload profile is considered complete.
During this period, new behaviour of the workload is added to the profile. After the period ends, the profile is finalized.
Default:
1hExamples:
learningPeriod: 1hlearningPeriod: 24h -
objectsettings.nodeAgent.nodeSelector
Labels of the nodes to run the eBPF agent on.
By default, the agent runs on every Linux node. Use this parameter to limit it to a subset of nodes, for example nodes whose kernels meet the BTF requirement.
Default:
{}Example:
node-role.kubernetes.io/worker: '' -
array of objectssettings.nodeAgent.tolerations
Tolerations for the eBPF agent DaemonSet.
The same as
spec.tolerationsfor the Kubernetes pod.If the parameter is not set, the agent tolerates the standard Deckhouse Platform (DP) taints: control plane and etcd arbiter taints,
dedicated.deckhouse.io,dedicated, cluster autoscaler and DRBD taints, and the keys from the globalcustomTolerationKeysparameter.Example:
tolerations: - operator: Exists-
stringsettings.nodeAgent.tolerations.effect
-
stringsettings.nodeAgent.tolerations.key
-
stringsettings.nodeAgent.tolerations.operator
-
integersettings.nodeAgent.tolerations.tolerationSeconds
-
stringsettings.nodeAgent.tolerations.value
-
-
-
objectsettings.nodeScanning
Configuration for node (host filesystem) vulnerability scanning.
This feature scans the host filesystem of each Kubernetes node to detect OS package vulnerabilities.
Default:
{}-
integersettings.nodeScanning.concurrentLimit
Maximum number of concurrent node scan jobs.
Each running node scan job uses up to 1 CPU and 2 GiB of memory on its node. A higher value increases the total load on the cluster.
Default:
1Allowed values:
1 <= XExamples:
concurrentLimit: 1concurrentLimit: 2concurrentLimit: 3 -
booleansettings.nodeScanning.enabled
Enables node vulnerability scanning.
When enabled, the operator scans the host filesystem of each node for OS package vulnerabilities. Results are stored in NodeVulnerabilityReport objects.
Default:
falseExamples:
enabled: trueenabled: false -
booleansettings.nodeScanning.hideUnfixedCVEs
Whether to report only vulnerabilities that have a fix available.
This reduces the report size but hides vulnerabilities that have no fix yet.
Default:
falseExamples:
hideUnfixedCVEs: truehideUnfixedCVEs: false -
objectsettings.nodeScanning.nodeSelector
Labels of the nodes to scan.
Only nodes that have all the listed labels are scanned.
Default:
{}Examples:
node-role.kubernetes.io/worker: ''env: production -
array of stringssettings.nodeScanning.pkgTypes
List of package types to include in node scanning:
OS: Operating system packages (rpm, deb, apk, etc.).Library: Application-level libraries (jars, npm modules, Python packages, etc.) found on the node filesystem.
Default:
[
 "OS"
]
Examples:
pkgTypes: - OSpkgTypes: - OS - Library-
stringsettings.nodeScanning.pkgTypes.Element of the array
Allowed values:
OS,Library
-
objectsettings.nodeScanning.resources
Resource
requests/limitsfor node scan jobs (scan-noderootfspods).Unlike
scanJobResources, each omitted field keeps its default value:100m/256Mirequests and1/2Gilimits. A default request above the limit you set is lowered to that limit. A ModuleConfig with an explicit request above the limit, set or default, is rejected. Zero values are not allowed.A scan of the entire node filesystem can take up to 2 GiB of memory, and a scan job that exceeds the memory limit is terminated (
OOMKilled) without a report. A lower CPU limit slows the scan down; raisenodeScanning.timeoutaccordingly. A request that does not fit the free resources of the node fails the job (OutOfmemory,OutOfcpu).Default:
{}Example:
limits: memory: 3Gi-
objectsettings.nodeScanning.resources.limits
Default:
{}-
stringsettings.nodeScanning.resources.limits.cpu
Default:
1Pattern:
^([1-9][0-9]*(\.[0-9]+)?|0\.[0-9]*[1-9][0-9]*)m?$Examples:
cpu: 500mcpu: '1' -
stringsettings.nodeScanning.resources.limits.memory
Default:
2GiPattern:
^([1-9][0-9]*(\.[0-9]+)?|0\.[0-9]*[1-9][0-9]*)(k|M|G|T|Ki|Mi|Gi|Ti)?$Examples:
memory: 1Gimemory: 2Gi
-
-
objectsettings.nodeScanning.resources.requests
Default:
{}-
stringsettings.nodeScanning.resources.requests.cpu
Default:
100mPattern:
^([1-9][0-9]*(\.[0-9]+)?|0\.[0-9]*[1-9][0-9]*)m?$Examples:
cpu: 100mcpu: 250m -
stringsettings.nodeScanning.resources.requests.memory
Default:
256MiPattern:
^([1-9][0-9]*(\.[0-9]+)?|0\.[0-9]*[1-9][0-9]*)(k|M|G|T|Ki|Mi|Gi|Ti)?$Examples:
memory: 256Mimemory: 512Mi
-
-
-
array of stringssettings.nodeScanning.scanners
List of scanners to enable on each node:
Vuln: Vulnerability scanner (matches known CVEs in OS and library packages of the node host filesystem).Secret: Secret scanner (detects hardcoded credentials such as AWS keys, GitHub tokens, etc. in files on the node).
Default:
[
 "Vuln"
]
Examples:
scanners: - Vulnscanners: - Vuln - Secret-
stringsettings.nodeScanning.scanners.Element of the array
Allowed values:
Vuln,Secret
-
array of stringssettings.nodeScanning.severities
Severity levels of vulnerabilities included in node vulnerability reports.
Warning. LOW and MEDIUM levels might increase total report size by an order of magnitude and valuable findings will become harder to spot. If
securityStorageForReportsisfalse, a report on a node with many packages can exceed the 3 MB object size limit ofetcd.Default:
[
 "CRITICAL",
 "HIGH"
]
Examples:
severities: - CRITICAL - HIGHseverities: - CRITICAL - HIGH - MEDIUM-
stringsettings.nodeScanning.severities.Element of the array
Allowed values:
UNKNOWN,LOW,MEDIUM,HIGH,CRITICAL
-
-
array of stringssettings.nodeScanning.skipDirsList of directories to skip during node scanning.
Default:
[ "/proc", "/sys", "/dev", "/run", "/var/lib/containerd", "/var/lib/docker", "/var/lib/kubelet/pods" ]Example:
skipDirs: - /proc - /sys - /dev -
stringsettings.nodeScanning.timeout
Timeout for node scan jobs.
If the parameter is not set, the timeout is 5 minutes.
Default:
‘’Examples:
timeout: 10mtimeout: 30m
-
-
objectsettings.nodeSelector
Node selector for the module components (the operator,
trivy-server,trivy-provider,registry-scanner,security-storageandreport-updater) and image scan jobs.The same as
spec.nodeSelectorfor the Kubernetes pod.Node scan jobs and the eBPF agent (
nodeAgent) do not use this parameter.If the parameter is omitted, it will be determined automatically.
Example:
disktype: ssd -
objectsettings.registryScanning
Configuration for periodic CVE scanning of container images stored in external registries.
Scan targets are defined in RegistryScanTarget objects, and scan results are stored in RegistryImageVulnerabilityReport objects.
Default:
{}-
integersettings.registryScanning.concurrentScansMaximum number of image scans that the registry scanner runs in parallel across all targets.
Default:
5Allowed values:
1 <= XExamples:
concurrentScans: 3concurrentScans: 5concurrentScans: 10 -
booleansettings.registryScanning.enabledEnables the registry CVE scanner.
Default:
falseExamples:
enabled: trueenabled: false
-
-
array of stringssettings.reportResourceLabels
List of labels of the scanned objects to copy to the module reports, such as VulnerabilityReport, ConfigAuditReport and RbacAssessmentReport.
A report gets each listed label with the value it has on the scanned object.
Examples:
reportResourceLabels: appreportResourceLabels: env -
objectsettings.scanJobResources
CPU and memory
requests/limitsof the Trivy container in image scan job pods.If the parameter is omitted, the module uses the default values:
100m/100Mrequests and500m/500Mlimits. If specified, only some of the fields may be set (for example, only memory). Unspecified fields are not filled in by the module.Node scan jobs are not affected.
Default:
{}Example:
limits: cpu: 500m memory: 500M requests: cpu: 100m memory: 100M-
objectsettings.scanJobResources.limitsResource limits of the Trivy container.
Default:
{}-
stringsettings.scanJobResources.limits.cpuCPU limit.
Examples:
cpu: 500mcpu: '1' -
stringsettings.scanJobResources.limits.memoryMemory limit.
Examples:
memory: 500Mmemory: 1Gi
-
-
objectsettings.scanJobResources.requestsResource requests of the Trivy container.
Default:
{}-
stringsettings.scanJobResources.requests.cpuCPU request.
Examples:
cpu: 100mcpu: 250m -
stringsettings.scanJobResources.requests.memoryMemory request.
Examples:
memory: 100Mmemory: 256Mi
-
-
-
objectsettings.scanPeriodsControls how often the operator rescans workloads and regenerates compliance reports.
Default:
{}-
stringsettings.scanPeriods.complianceRescanCron
Cron schedule that controls how frequently ClusterComplianceReport objects are regenerated.
Uses standard five-field cron syntax (
minute hour day-of-month month day-of-week).Default:
0 */6 * * *Pattern:
^(((([\*]{1}){1})|((\*\/){0,1}(([0-9]{1}){1}|(([1-5]{1}){1}([0-9]{1}){1}){1}))) ((([\*]{1}){1})|((\*\/){0,1}(([0-9]{1}){1}|(([1]{1}){1}([0-9]{1}){1}){1}|([2]{1}){1}([0-3]{1}){1}))) ((([\*]{1}){1})|((\*\/){0,1}(([1-9]{1}){1}|(([1-2]{1}){1}([0-9]{1}){1}){1}|([3]{1}){1}([0-1]{1}){1}))) ((([\*]{1}){1})|((\*\/){0,1}(([1-9]{1}){1}|(([1-2]{1}){1}([0-9]{1}){1}){1}|([3]{1}){1}([0-1]{1}){1}))|(jan|feb|mar|apr|may|jun|jul|aug|sep|okt|nov|dec)) ((([\*]{1}){1})|((\*\/){0,1}(([0-7]{1}){1}))|(sun|mon|tue|wed|thu|fri|sat)))$Examples:
complianceRescanCron: 0 0 * * satcomplianceRescanCron: 0 */6 * * * -
stringsettings.scanPeriods.workloadRescanPeriod
Maximum age of a vulnerability report before it is considered stale and queued for rescanning.
Once a report exceeds this age, the operator deletes it and schedules a new scan job to regenerate it. Set to
""to disable periodic rescanning entirely (reports are generated once and never refreshed automatically).Default:
24hPattern:
^([0-9]+h)?([0-9]+m)?([0-9]+s)?$Examples:
workloadRescanPeriod: 2h50m30sworkloadRescanPeriod: 12h30mworkloadRescanPeriod: 24h
-
-
objectsettings.securityEvents
Settings of the security events the module sends to the
security-events-managermodule.The events are created only when the
security-events-managermodule is enabled.Default:
{}-
stringsettings.securityEvents.minimumSeverity
Lowest finding severity that produces a security event.
A scan report produces an event when its most severe finding is at this level or above, and the event takes the severity of that finding. The parameter applies to vulnerabilities in workloads, nodes and registry images, exposed secrets, misconfigurations and RBAC issues. Rejected images, registry scan failures and failed compliance controls always produce an event.
A report with LOW or UNKNOWN findings only counts as LOW.
Default:
HIGHAllowed values:
CRITICAL,HIGH,MEDIUM,LOWExamples:
minimumSeverity: HIGHminimumSeverity: CRITICALminimumSeverity: LOW
-
-
booleansettings.securityStorageForReports
Stores scan reports in
security-storageinstead ofetcd.If
true, reports are served by thesecurity-storageaggregated API server under thetrivy.deckhouse.ioAPI group and are not limited by theetcdobject size. Iffalse, reports are stored inetcdas custom resources of theaquasecurity.github.ioAPI group.Warning. Changing the value does not move existing reports. The operator rescans workloads and nodes and recreates the reports in the new storage.
Default:
trueExamples:
securityStorageForReports: truesecurityStorageForReports: false -
integersettings.securityStoragePVCRequest
Size of the PersistentVolumeClaim used by
security-storageto store scan results, in GiB.The claim is never shrunk: if the existing claim requests more than the value, the module keeps its size. The module expands a smaller claim only if its StorageClass allows volume expansion. The parameter has no effect if
apiServerStorageClassis"false".Default:
10Allowed values:
1 <= X -
array of stringssettings.severitiesSeverity levels of vulnerabilities included in vulnerability reports.
Default:
[ "UNKNOWN", "LOW", "MEDIUM", "HIGH", "CRITICAL" ]Examples:
severities: - CRITICAL - HIGH - MEDIUM - LOW - UNKNOWNseverities: - CRITICAL - HIGH-
stringsettings.severities.Element of the array
Allowed values:
UNKNOWN,LOW,MEDIUM,HIGH,CRITICAL
-
-
stringsettings.storageClass
Name of the StorageClass used to store the module data.
If the value is not specified, the StorageClass will be used according to the global storageClass parameter setting.
The global
storageClassparameter is only considered when the module is enabled. Changing the globalstorageClassparameter while the module is enabled will not trigger disk re-provisioning.Warning. Specifying a value different from the one currently used (in the existing PVC) will result in disk re-provisioning and all data will be deleted.
If
falseis specified,emptyDirwill be forced to be used.Examples:
storageClass: ceph-ssdstorageClass: 'false' -
array of objectssettings.tolerations
Tolerations for the module components: the operator,
trivy-server,trivy-provider,registry-scanner,security-storageandreport-updater.The same as
spec.tolerationsfor the Kubernetes pod.Scan jobs and the eBPF agent (
nodeAgent) do not use this parameter.If the parameter is omitted, it will be determined automatically.
Example:
tolerations: - effect: NoSchedule key: key1 operator: Equal value: value1-
stringsettings.tolerations.effect
-
stringsettings.tolerations.key
-
stringsettings.tolerations.operator
-
integersettings.tolerations.tolerationSeconds
-
stringsettings.tolerations.value
-
-
booleansettings.useVEXFromOCI
Enables the use of VEX attestations of the scanned images stored in the OCI registry.
Vulnerabilities declared in the attestations are not reported. The attestations are fetched with the certificates from
additionalRegistryCA. Images from the registries ininsecureRegistries, and in registry scanning images of a RegistryScanTarget withinsecure: true, are scanned without VEX attestations.Default:
falseExamples:
useVEXFromOCI: trueuseVEXFromOCI: false -
stringsettings.vulnerabilityDatabaseMaxAge
Maximum age of the Trivy vulnerability database (
trivy-db) before theTrivyVulnerabilityDatabaseOutdatedalert fires.Age is measured from the database
UpdatedAttimestamp published in thetrivy-db-infoConfigMap by thetrivy-db-infosidecar (onlytrivy-dbis checked;trivy-java-dbis not).The related
TrivyVulnerabilityDatabaseMissingalert fires when that ConfigMap is absent or has notrivy-db.updatedAtfor 30 minutes (for example, registry/network issues or an incomplete air-gapped installation).Set to
""to disable both database freshness alerts (outdated and missing). Zero durations such as0sor0hare invalid — use""to disable.Default:
168hPattern:
^(?:[0-9]*[1-9][0-9]*h(?:[0-9]+m)?(?:[0-9]+s)?|(?:[0-9]+h)?[0-9]*[1-9][0-9]*m(?:[0-9]+s)?|(?:[0-9]+h)?(?:[0-9]+m)?[0-9]*[1-9][0-9]*s)?$Examples:
vulnerabilityDatabaseMaxAge: 168hvulnerabilityDatabaseMaxAge: 336hvulnerabilityDatabaseMaxAge: 720hvulnerabilityDatabaseMaxAge: ''
-